Code of Conduct: Our Code of Values & Quality Promise
1. Preamble & Self-Image
CyberCompare stands for cybersecurity that is comprehensible, effective, and economical. Started as an initiative within the Bosch Group and now operating as an independent entity, we accompany organizations and companies across all industries as a holistic partner in security management throughout the entire lifecycle:
“We assume responsibility for security: From strategy and vendor selection through to implementation and interim management.”
At our core is always our objectivity: We do not enter into sales or reselling agreements with other vendors and do not sell our own products or managed services. We view ourselves as architects and engineers, committed to independence and acting as a fiduciary agent in our clients’ interest.
Our roots in a world-leading industrial and technology group continue to shape our foundation today: The highest standards of reliability, data security, engineering precision, and lived compliance. As an independent company, we combine these values with maximum agility, entrepreneurial freedom, and uncompromising customer focus.
As we expand our service portfolio, our responsibility grows. This Code of Conduct defines the binding principles of our actions towards clients, technology providers, and service providers. It ensures that objectivity, confidentiality, and strict client loyalty are the top priority in every phase of our collaboration.
2. Our Four Pillars of Performance: Responsibility in Practice
We structure our services along four core areas. Clear standards of integrity and quality apply in each area:
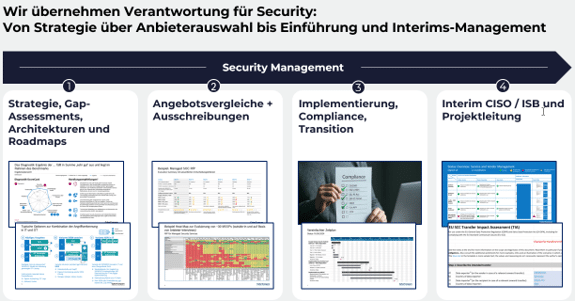
2.1 Pillar 1: Strategy, Gap Assessments, Architectures, and Roadmaps
Needs-Based Diagnostics Instead of Over-Engineering: Our 360° assessments, diagnostic scorecards, and roadmaps are strictly aligned with the client’s actual risk profile and resources – not with the sales targets of third parties.
Architectural and Technological Neutrality: When designing security architectures (e.g., options for IT/OT threat detection via SOC, SIEM, or XDR), we recommend solutions based on functional and technical value, not on brand preferences.
Honest Recommendations: If existing tools and processes are already sufficient, or if organizational measures are preferable to new technical acquisitions, we communicate this openly and transparently.
2.2 Pillar 2: Bid Comparisons and RFPs (Tendering)
Market Breadth and Equal Opportunity: We include established market leaders as well as innovative specialists. Any vendors favored by the client are also included in the comparison without bias.
Objective Evaluation Matrix: Tenders (e.g., Managed SOC RFPs) and evaluation heatmaps are based on standardized, transparent criteria (including capability, price-performance ratio, service levels, interface compatibility, and references).
Anonymized Protection: To protect our clients’ confidential business data and negotiating positions, we conduct procurement and tendering processes completely anonymously upon request.
2.3 Pillar 3: Implementation, Compliance, and Transition
Regulatory Integrity: In compliance projects (e.g., NIS2, ISO/IEC 27001, GDPR, EU AI Act, BSI standards, TIA/AVV), we align ourselves with recognized standards and best practices. We do not create formal “paper tigers,” but rather resilient, auditable management systems.
Reliable Transition: When introducing new security solutions (e.g., EDR rollout, MSSP onboarding), we ensure uninterrupted operations through structured schedules and clear milestones.
Focus on Empowerment: The goal of every implementation is the sustainable empowerment of the client’s own organization. We build knowledge transfer rather than artificial dependencies.
2.4 Pillar 4: Interim CISO / ISO and Project Management
Unrestricted Client Loyalty: As an Interim CISO, Information Security Officer (ISO), or external project lead, we act exclusively in the interest of the client organization and its security objectives.
Neutral Vendor & Service Management: In ongoing service provider and partner management, we evaluate performance data, SLA compliance, and incident responses without bias, demanding quality on behalf of our client.
Pragmatism with Foresight: We steer security projects with operational sound judgment, prioritize critical risks, and translate security requirements comprehensibly for executive management and business departments.
3. The Six Fundamental Pillars of Our Actions
I. Independence & Neutrality
CyberCompare acts 100% independently in the client’s interest. No provider of security software, hardware, or managed services holds shares in our company or exerts influence on our evaluations and recommendations. Our decisions and advisory results are free from manufacturer interests and third-party corporate guidelines – we are committed solely to the protection and success of our clients.
II. Transparency & Traceability
We fully disclose the standards of our evaluations, comparison matrices, and diagnostics to our clients. Clients receive all original documents from providers with contact details, as well as our evaluation documents with weighted ratings for each criterion. Every recommendation must be technically, operationally, and economically justified for the client.
III. Confidentiality & Data Sovereignty
Security data, infrastructure topologies, and vulnerability analyses are among a company’s most sensitive information. We treat all client data at least under the confidentiality and security standards that we apply to our own data. Client-specific tender documents will never be made accessible to third parties without explicit release.
IV. Fair Competition
We meet all market players with fairness, respect, and professionalism. Selection decisions are based exclusively on performance, reliability, support quality, and economic suitability.
VI. Efficiency & Sustainability
Security must remain affordable and practical. We measure our success by ensuring that our clients achieve the maximum level of protection for their defined budget – without superfluous license costs or operational friction losses.
4. Commitment & Contact Persons
This Code of Conduct is binding for all employees, consultants, and associated experts of CyberCompare.
For questions regarding our Code of Conduct, reports of violations, or suggestions for further development, our management team is available at any time:
Email: contact@cybercompare.com
Company: CyberCompare GmbH